Protecting your privacy is a fundamental component of our service. We have been committed to maintaining the confidentiality, integrity and security of Personal Data entrusted to us by you.
Article 5 of the GDPR states that personal data must be processed lawfully, fairly, and in a transparent manner. This Privacy Notice explains why and how we collect, process, and destroy your data. Please read the following carefully to understand our views and practices, and do not hesitate to reach out if you have any questions.
Leo is subject to several regulatory regimes including: the UK General Data Protection Regulation (GDPR), as amended in 2025 by the Data (Use and Access) Act 2025 (DUAA)[1], the EEA GDPR, and where applicable, US Privacy Notice (see Schedule 2). The UK GDPR and DUAA apply when we process personal data of individuals in the UK, and the EEA GDPR applies when we process personal data of individuals in the EEA. Similarly, where Leo processes personal data of individuals in the United States, applicable US federal and state privacy law may apply; see Schedule 2 (US Privacy Notice) below, including a summary of Leo’s role as a service provider to its US financial-institution clients..
For purposes of this Privacy Notice, the following terms will be defined as follows:
“Information Commission” also known as the “Information Commissioner’s Office” or “ICO”
“Legitimate Interest” refers to when we process personal data that is necessary for our legitimate interests or those of a third party, provided those interests are not overridden by your rights and freedoms.
“Legitimate Interest Assessment” or “LIA” is a careful review to ensure that i) the interest pursued is legitimate; ii) the processing is necessary; and iii) your rights and freedoms are appropriately protected.
“Recognised Legitimate Interest” is a statutory category where Parliament has already determined that the balancing test is satisfied, and we are not required to conduct a separate LIA.[2]
“Personal Data” or “Personal Information” means any information about an individual from which that person can be identified. Personal Data and/or Personal Information does not include data where the identity has been removed (i.e. anonymous data).
“Special Categories” means more sensitive personal data which require a higher level of protection, such as information about a person’s health, sexual orientation, political views etc. For the full list please refer to Article 9 of the EEA&UK GDPR.
“Data Subject” refers to any individual person who can be identified, directly or indirectly, via an identifier such as name, ID number or location data.
Leo RegTech Limited is registered at 11 Old Jewry, EC2R 8DU with company number 04829021 (“Leo”).
If you are a Leo employee, vendor, or client, we act as the data controller under GDPR. This means that we determine the means and purposes of processing your personal data. If you are a user of the Leo app and you provide us with Personal Data in the Leo App, we act as a data processor. This means we process such personal information based on the written instructions of a data controller, which is you- Leo’s direct client.
Please refer to the table in Schedule 1 below.
We process your personal data in accordance with the UK GDPR as amended by the Data (Use and Access) Act 2025 (“DUAA”). The lawful basis we rely on depends on the nature of the processing and the context in which your data is collected.
We may process your personal data where you have given clear and informed consent. You may withdraw your consent at any time. Withdrawal does not affect the lawfulness of processing carried out before consent was withdrawn.
We process personal data where it is necessary to enter into or perform a contract with you, including providing services, managing your account, and responding to service‑related requests.
We process personal data where required to comply with UK law or regulatory obligations, including obligations under financial services regulation, anti‑money laundering requirements, tax law, and statutory reporting.
We may process personal data where necessary to protect someone’s life or prevent serious harm.
Where applicable, we may process personal data to perform tasks carried out in the public interest or in the exercise of official authority.
If you wish to review, change or update the Personal Data that you have provided to us; request removal from a mailing list; or address any other privacy concerns you may have, please contact us at [email protected]. Please note that you can review your direct marketing preferences by clicking the unsubscribe button in any of Leo marketing emails.
We will not share Personal Data about you with third parties unless we are required to do so by law or if we use well established and trusted services providers.
The service providers that we share your personal data with are:
Leo does not transfer your personal information outside of the European Economic Area (EEA). If an international transfer becomes necessary, such as for a UK employee background check, we will transfer your personal data to countries outside the United Kingdom using safeguards that comply with the UK GDPR as amended by the Data (Use and Access) Act 2025. Such safeguards may include:
Adequacy Decisions
Where the UK Government has determined that a country ensures an adequate level of protection for personal data, we may rely on that decision to transfer your data. Under the DUAA, this determination (and any transfer made under appropriate safeguards, such as the UK IDTA) is assessed using a new “data protection test”: the standard of protection in the destination country or under the relevant safeguard must be “not materially lower” than the equivalent standard under the UK GDPR, replacing the earlier “essentially equivalent” test.
Appropriate Safeguards
If a country is not covered by an adequacy decision, we use one or more of the following safeguards:
We also assess whether additional technical, contractual, or organisational measures are needed to ensure your data remains protected.
Transfer Risk Assessments
Where required, we carry out a transfer risk assessment (TRA) to evaluate the laws and practices of the destination country and ensure that your rights remain protected.
Your Rights
You may contact us for more information about the safeguards we use for international transfers or to request a copy of the relevant transfer mechanism.
We will keep your personal data for no longer than is reasonably necessary, either due to legal obligations or legitimate business interests.
Your Rights:
Additional Information:
How to Exercise Your Rights:
If we need to process your data for purposes other than the original reason it was collected, Leo will only do so if the new processing is compatible with the original purpose or if the personal data is anonymised and cannot be re-identified.
Maintaining data security means ensuring the confidentiality, integrity, and availability of personal data for authorised purposes.
Leo has implemented appropriate security measures to prevent your personal data from being accidentally lost, used, accessed in an unauthorised way, altered, or disclosed. We limit access to your personal data to employees, agents, contractors, and other third parties on a need-to-know basis. They will only process your personal data on our instructions and are bound by a duty of confidentiality.
Leo will only transfer personal data to a third party if they agree to comply with our procedures and policies or put in place adequate measures before receiving it.
We have established procedures to handle any suspected personal data breaches and will notify you and any applicable regulators of a breach where we are legally required to do so.
For information on how Leo safeguards personal data processed through AI systems, please contact us at [email protected].
In certain cases, and only as permitted by law, we may control and process personal data that is more sensitive in nature. For example, this applies when we provide Leo’s modules for Know Your Client (KYC) / Anti-Money Laundering (AML) checks or client/vendor onboarding. These modules may also store information on past criminal convictions.
When we process your personal data based on legitimate interest, we have carried out a Legitimate Interests’ Assessment (LIA) to ensure that we have considered your interests, and any risks posed to you against our own interests. This ensures that such interests are proportionate and appropriate for purposes such as HR, marketing, and day-to-day operations. Please see Schedule 1 of this Privacy Notice for more details of which business processes use legitimate interest as legal basis for processing.
This may be applied when necessary or appropriate under the circumstances to comply with law or regulation. In such cases an LIA does not need to be conducted. Examples of recognised legitimate interests include: safeguarding; national security; crime prevention; and certain public‑interest or regulatory functions, among others.
When sending marketing materials to customers, we may rely on either your consent or our legitimate interest.
We only use legitimate interest for marketing if we have assessed that the information being sent is beneficial to you, have weighed our interests against yours, and determined that there is minimal risk posed. The method and content must be non-intrusive and something you would typically expect to receive.
Our customer relations management system notifies us when you open an email from us and when you click a link inside, allowing us to build meaningful connections with you. If you do not want to share this information with us, please click ‘Unsubscribe’ at the bottom of any email communication from Leo.
Cookies are small text files which are transferred from this website and stored on your device. We use cookies to help us provide you with a personalised service, and to help make our website, applications and services better for you.
We provide the following information with some explanations to ensure transparency to our users:
Should you wish to change your preferences regarding cookies, please hit an icon in the bottom left corner of the website.
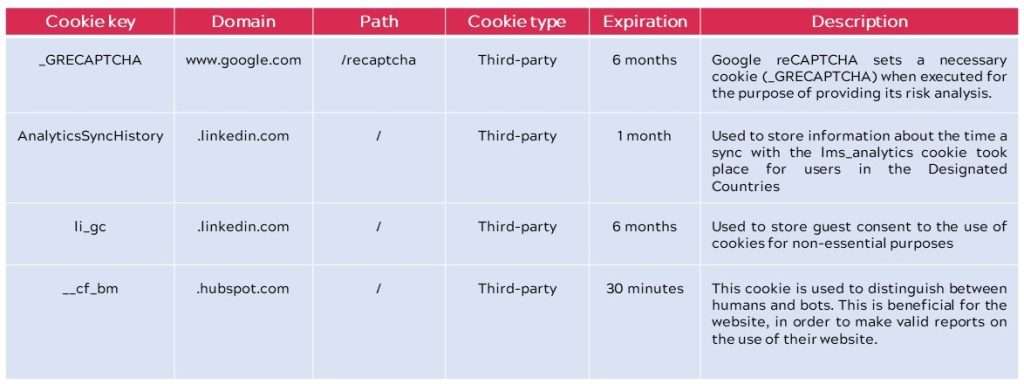
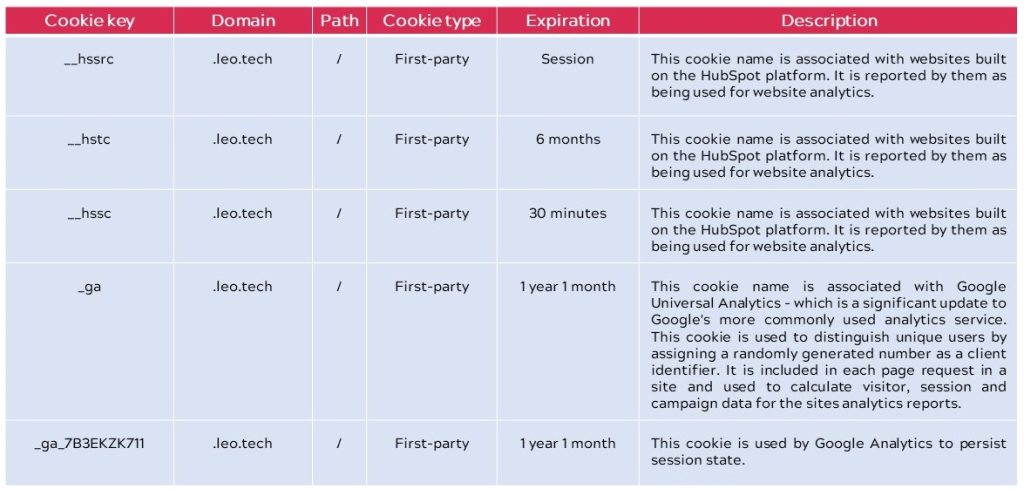
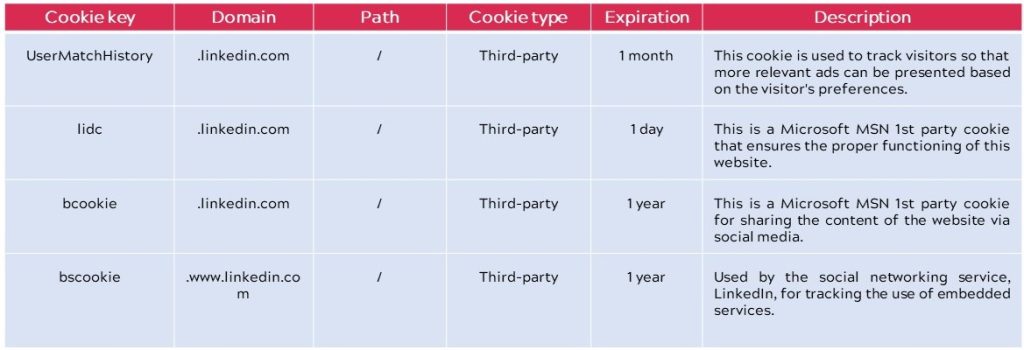
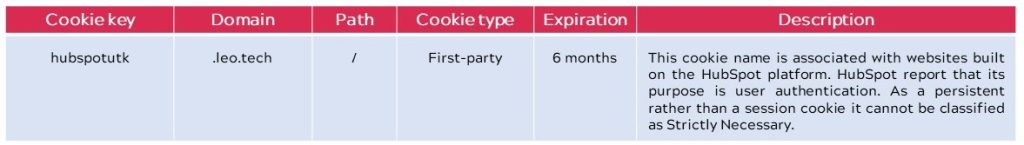
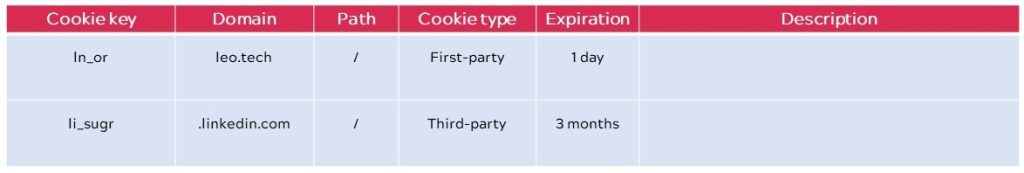
Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team understand which sections of the website you find most interesting and useful.
Cookie Category | Purpose / Description | Default Status | Specific Cookies & Retention |
Strictly Necessary | Necessary for the website’s core functionality, including remembering your cookie preferences. These cookies do not require consent and cannot be disabled. | Always Enabled | See images above |
Analytics (Google Analytics) | Collects anonymous information such as the number of visitors to the site and the most popular pages, to help us understand site usage and improve the website. | Enabled by default; can be switched off in cookie settings | See images above |
Any changes we may make to our Privacy Policy in the future will be posted on this page and, where appropriate, notified to you by email.
SCHEDULE 1
What types of Personal Data do we collect, for what purpose and on what lawful basis?
| PURPOSE FOR WHICH PERSONAL DATA WAS COLLECTD | TYPES OF PERSONAL DATA COLLECTED | LEGAL BASIS FOR PROCESSING OF PERSONAL DATA |
| Marketing | Name, email address, direct phone numbers, associated company name, IP addresses. | Legitimate interest: advancement of Leo’s business by targeting well researched audience who would benefit from the services offered. |
| Client relations | Name, email address, direct phone numbers, associated company names, IP addresses, marriage status, interests, and content of emails. | Legitimate interest: Communication with clients and client relationship management proportionate to the services provided. |
| Credit control | Name, email, company address, outcome of credit control. | Legitimate interest: Contracting with credit-worthy businesses not to expose Leo to credit risks |
| Recruitment | Name, residential address, contact details, interview notes, CV contents, salary expectations, D.O.B., nationality, and mother’s maiden name. | Legitimate interest: Talent acquisition and management of the recruitment process in relation to individuals interested in working with Leo. |
| Invoicing | Name and contact details at an associated company. | Legitimate interest: Charging fees, including final invoices after the contract termination |
| Provision of Leo’s services | Log in details, name, contact number, roles and names, email addresses. | Legitimate interest: Processing of personal data is necessary for the provision of services, including post-contract termination. The latter processing is done in accordance with contractual provisions. |
| Prospecting | Name, email address, direct phone numbers, associated company names , IP addresses, personal information such as hobbies, that may be revealed by the prospect and noted by Leo’s sales representative as relevant to the prospecting process. | Legitimate interest: advancement of Leo’s business by targeting well researched audience who would benefit from the services offered and entering into prospecting processes with individuals interested in Leo services. |
| Third party management | Name, contact details, and associated company. | Legitimate interest: Management of Leo’s business relationships with third parties like suppliers and strategic partners. |
| Meeting HMRC requirements | Name, contact details and associated accounting data. | Legal obligation. |
| ID Verification Service | Name, photograph of the face, nationality, passport number. | We act here as data processor and therefore we conduct the processing upon your instructions if you purchased the service. |
| AML Background Checks | Name and publicly available data associated with the search. | We act here as data processor and therefore we conduct the processing upon your instructions if you purchased the service. |
| Data entered into Leo by clients | Roles and names, phone numbers, addresses associated with the BCP; name, previous names, position within firm, other directorships, references, NIN, home address, history of residential addresses, certified copies of: passport, proof of address; CV; criminal proceedings information; civil proceedings information; other relevant matters; disciplinary matters; potential complaints against person; potential disqualification or reprimand by the FCA or other regulatory body; nationality, shareholding, country of residence; names, address, PEP status of PSCs and clients complaints; training records. | We act here as data processor and therefore we conduct the processing upon your instructions if you purchased the service. |
| Sharing data for marketing purposes | Names, roles, email addresses, and corporate phone numbers in the B2B environment. | Legitimate interest: advancement of Leo’s business by sharing Leo’s leads with carefully chosen partners. |
This Schedule applies to personal data of individuals located in the United States that Leo processes directly in its own right — for example, prospective and existing point-of-contact individuals at US clients, marketing contacts, website visitors, job applicants, and Leo’s own US-based personnel. It does not apply to personal data that Leo processes solely as a service provider on behalf of a US financial-institution client (see “Relationship to GLBA” below).
The substantive protections described elsewhere in this Privacy Notice — including how we collect, use, and safeguard personal data, and how to contact us — apply equally here. This Schedule focuses only on the points where US federal or state law gives you rights, or imposes obligations on Leo, that go beyond, or differ from, the UK GDPR and EEA GDPR framework described above.
Many of Leo’s clients — asset managers, investment advisers, broker-dealers, and marketers — are themselves “financial institutions” for the purposes of the Gramm-Leach-Bliley Act (GLBA). Where Leo processes nonpublic personal information (NPI) on their behalf, Leo does so as a service provider or non-affiliated third party, under contractual confidentiality, use-limitation, and safeguards obligations consistent with GLBA and its implementing regulations (as applicable to the client: SEC Regulation S-P, 17 CFR Part 248; the FTC Privacy Rule, 16 CFR Part 313; or Regulation P, 12 CFR Part 1016).
The obligation to issue GLBA privacy notices to individual customers, and to honor GLBA opt-out rights, remains with Leo’s financial-institution client as the data controller of that relationship — not with Leo. Personal data processed under this GLBA framework is also generally exempt, at the entity or data level, from the state comprehensive privacy laws summarized below.
Please refer to Schedule 1 above for a full inventory of the personal data Leo collects and the purposes for which it is used. In summary, and using the terminology of US state privacy statutes, this includes identifiers (such as name and contact details), commercial information, internet or other electronic network activity information, professional or employment-related information, and inferences drawn from the foregoing.
Leo does not sell personal information, and does not share personal information for cross-context behavioral advertising, as those terms are defined under applicable US state privacy laws.
If you are a resident of a US state with a comprehensive consumer privacy law — for example, California (CCPA/CPRA), Virginia (VCDPA), Colorado (CPA), Connecticut (CTDPA), or the other states that have since adopted similar statutes — you have the rights described elsewhere in this Notice (access, correction, deletion, and portability), and in addition the following rights, which are not features of the UK GDPR or EEA GDPR:
US state privacy laws generally require a response within 45 days of receipt of a verifiable request, extendable by a further 45 days where reasonably necessary, with notice to you of the extension. This timeframe differs from the one-month period (extendable by a further two months for complex requests) that applies under the UK and EEA GDPR. We will take reasonable steps to verify your identity, or the authority of your agent, before acting on a request, consistent with the sensitivity of the personal data involved.
California Civil Code § 1798.83 gives California residents the right to request information once a year about disclosures of personal information Leo has made, if any, to third parties for those third parties’ own direct marketing purposes in the preceding calendar year. This right does not have a direct equivalent in the UK or EEA GDPR. Leo does not disclose personal information to third parties for their own direct marketing purposes; you may still submit a request using the contact details below.
Leo does not knowingly collect personal information from children under 13 (or under 16 in states that set a higher age threshold for the sale or sharing of personal information, such as California). If you believe a child has provided us with personal information, please contact us using the details below so we can address it.
In addition to the UK and EEA GDPR’s breach-notification framework described above, all US states have their own data breach notification statutes. These generally require notice to affected individuals and, in some cases, to state regulators, “without unreasonable delay” or within a fixed number of days following discovery of a breach (commonly 30 to 90 days, depending on the state), which may differ from the 72-hour regulator notification standard under the UK and EEA GDPR. Leo will comply with the applicable notification timeframe for the jurisdiction in question.
To exercise any of the rights described in this Schedule, please contact us at [email protected]. We will not charge a fee to process or respond to your request unless it is excessive, repetitive, or manifestly unfounded, in which case we may charge a reasonable fee or decline to act on the request, as permitted by applicable law.
References
[1] Data (Use and Access) Act 2025, c.18 (Royal Assent 19 June 2025). The Part 5 data protection reforms referenced in this Notice — including recognised legitimate interests (new Annex 1, UK GDPR), the revised Article 22A–22D regime for automated decision-making, and the “not materially lower” data protection test for international transfers (Chapter V, UK GDPR) — came into force on 5 February 2026 under the Data (Use and Access) Act 2025 (Commencement No. 6 and Transitional and Saving Provisions) Regulations 2026 (SI 2026/82). The data subject complaints duty in new section 164A of the Data Protection Act 2018 (inserted by section 103 of the Act) came into force on 19 June 2026. All of the foregoing provisions are, accordingly, now in force as of the date of this Notice.
[2] “Recognised legitimate interests” is a new lawful basis under Article 6(1) UK GDPR, set out in new Annex 1 UK GDPR (inserted by section 70 and Schedule 4, Data (Use and Access) Act 2025), in force from 5 February 2026.
[3] Section 164A, Data Protection Act 2018 (inserted by section 103, Data (Use and Access) Act 2025), in force from 19 June 2026. This right to complain directly to Leo as controller exists alongside, and does not replace, the right to complain to the Information Commissioner under section 165 of the Data Protection Act 2018.
[4] Articles 22A–22D, UK GDPR (inserted by section 80 and Schedule 6, Data (Use and Access) Act 2025), in force from 5 February 2026. These provisions replace the former Article 22 prohibition on solely automated decision-making with a permission-plus-safeguards model.